Since a journal website carries the scholarly record, it must remain safe, reachable and unchanged in its addresses over many years. Here is a practical checklist for running it: choosing a domain and host, HTTPS, software updates, the 3-2-1 backup rule, access control, risks like spam and cloned sites, monitoring, article landing pages, stable URLs and a maintenance calendar. Treat it as a routine to revisit, not a one-off task.
Why Operations Matter
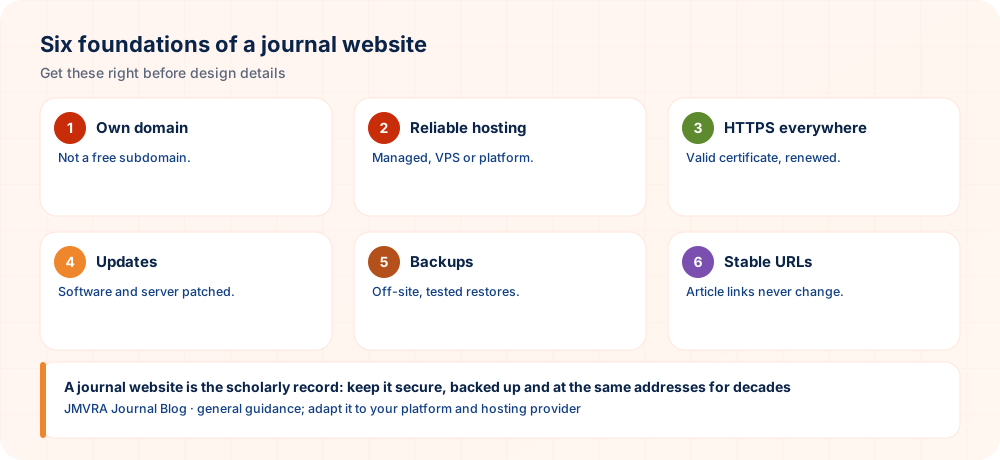
A journal website is more than a brochure: it is where the scholarly record is kept. Content, design and SEO are dealt with in academic journal website: required pages and SEO. This checklist addresses the operational side — hosting, security and maintenance — which determines whether the site is still safe and functioning in ten years.
Domain and Hosting
| Option | Good for | Watch out for |
|---|---|---|
| Shared hosting | Tiny sites with light traffic | Little control; disruptive neighbours |
| VPS or cloud server | Journals that have technical staff | Updates and security are your responsibility |
| Managed journal hosting | Journals that lack technical staff | Contract terms, data export and an exit plan |
| Journal management platform | Journals that want workflow together with hosting | Who holds control of the domain and data |
Register the journal’s own domain in the name of the journal or its publisher, renew it well before it expires and share the login details among more than one responsible person. Free subdomains appear untrustworthy and may vanish.
HTTPS Everywhere
Deliver every page over HTTPS with a valid certificate (free ones exist, for instance from Let’s Encrypt), redirect HTTP traffic to HTTPS and keep an eye on renewals. Login and submission pages must never operate without encryption. An expired certificate scares visitors away, so set a reminder well in advance.
Keep Software Updated
Most website compromises take advantage of flaws that are publicly known and already patched. Update the journal platform, plugins, themes, PHP or any other runtime, the database and the server operating system. Rehearse big upgrades on a duplicate site before going live. The OWASP Top 10 outlines the web application risks seen most often.
Backups You Can Restore
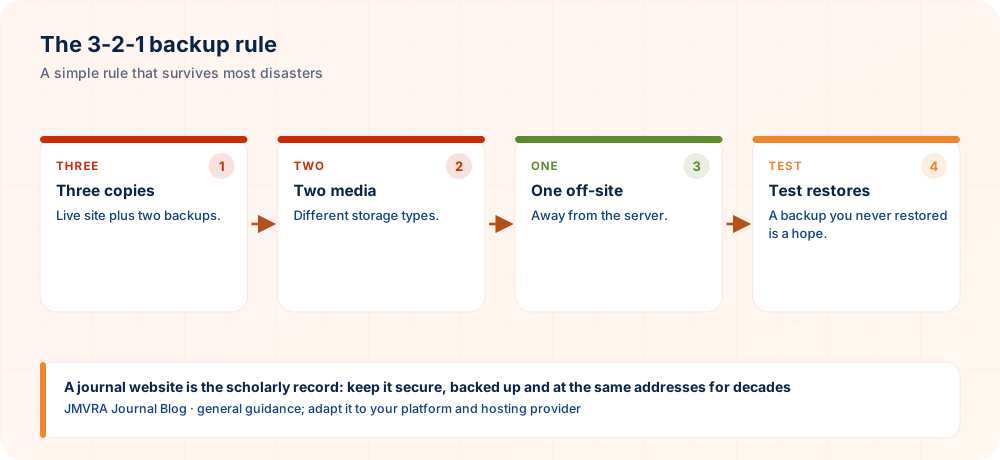
Back up the database, the uploaded files (manuscripts, PDFs, images) and the configuration. Store at least one copy away from the server and outside the hosting account, and run a full restore test on a regular basis. Backups also back up the journal’s archiving commitments; read repositories and journal archiving.
Access Control
- Give each editor and staff member an individual account; no shared logins.
- Require strong passwords and two-factor authentication for administrators.
- Least privilege: assign everyone only the role they need.
- Delete accounts quickly once people leave the board or the staff.
- Store manuscript files outside the public web root.
Threats and Defences
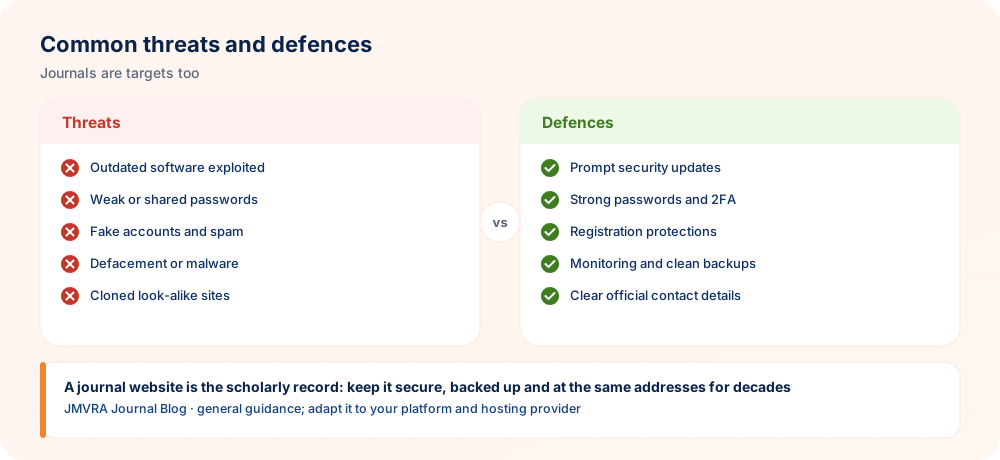
Journal sites often attract fake registrations, spam submissions and bots, so use safeguards such as CAPTCHAs and email confirmation. Fraudsters also clone journals: state your official domain, ISSN and contact details clearly so that authors can check them. Read how to spot hijacked journals.
Monitoring
Set up uptime monitoring with alerts, inspect server and application error logs, look out for unexpected new admin accounts or file changes, and make sure scheduled tasks (emails, reminders, DOI deposits) really do run.
Article Landing Pages
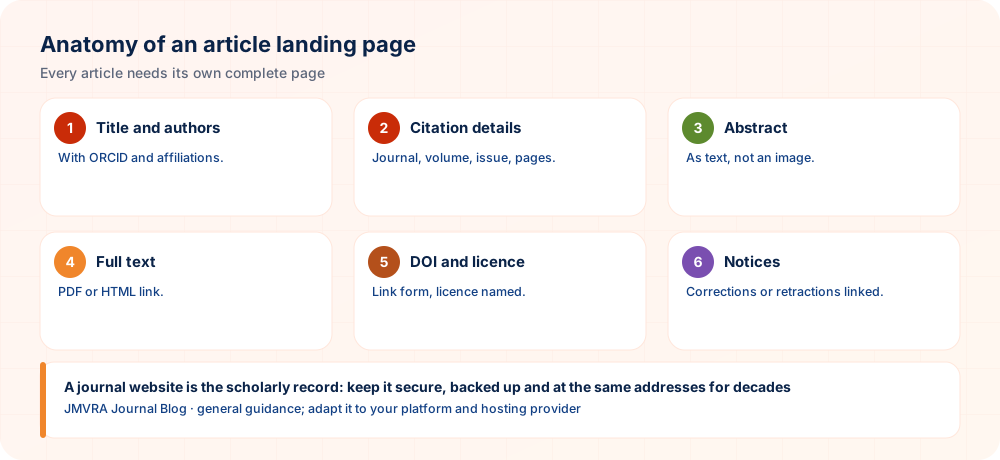
Every article deserves a permanent page of its own, showing the full citation, an abstract, the full text, the DOI as a clickable link, the licence and any correction or retraction notices. Citation meta tags for Google Scholar belong there too; see the journal article metadata checklist. A manual check of a few pages after each issue catches missing fields early.
Keep URLs Stable
Addresses of articles and issues are cited in theses, papers and databases, so do not restructure them lightly. If a redesign or a platform migration forces a change, set up permanent (301) redirects from each old address and update the DOI resource URLs at the same moment; see Crossref DOI registration for journals.
Maintenance Calendar
| How often | Tasks |
|---|---|
| Weekly | Install security updates; confirm backups ran; read the error logs |
| Monthly | Restore a recent backup as a test; go over user accounts; confirm scheduled tasks run |
| Each issue | Make sure new article pages, PDFs, meta tags and DOIs resolve |
| Quarterly | Run a link check; review plugins and delete unused ones |
| Yearly | Renew the domain and contracts; review hosting; audit board and policy pages |
Mistakes to Avoid
- A domain registered in one individual’s private account and later lost.
- Years pass after installation without any updates.
- Backups kept solely on the same server.
- Article URLs altered during a redesign with no redirects.
- Shared admin passwords sent around by email.
JMVRA’s Approach
Under JMVRA’s archival policy, every article keeps the URL it first had, issue pages are permanent, and retracted papers remain visible with a marking. On the journal verification page, authors can check JMVRA’s real website and contact details. Journal owners can turn to the network’s new journal guide for launch and DOIs, and to the OJS setup guide for platform configuration.
JMVRA in brief
- Review: transparent, double-blind peer review, normally by at least two subject experts. Specialist reviewers assess your paper, and you receive the acceptance or rejection decision by email and WhatsApp.
- Fee: A payment of ₹971 INR (Indian authors) or $41 USD (foreign authors) falls due only on acceptance, and submission and review are free of charge.
- Access: ISSN 2984-8911; readers get open access with a CC BY 4.0 licence; new issues monthly; you may submit whenever suits you; Crossref DOI offered on request.
- Indexing: JMVRA appears in Google Scholar and is registered with Crossref and the ISSN Portal / ROAD; it is not currently indexed in Scopus, Web of Science or DOAJ.
Share Your Research Through JMVRA
Have your work published in JMVRA
JMVRA (ISSN 2984-8911) is a peer-reviewed, open access journal spanning many disciplines. Submission is free. Specialist reviewers assess your paper, and you receive the acceptance or rejection decision by email and WhatsApp.
- 1. Match your manuscript to the guidelines
- 2. Submit online
- 3. Peer review
- 4. Decision by email & WhatsApp
- 5. Appear in open access
Your At-a-Glance Checklist
- DomainJournal-owned
- HTTPSEverywhere
- UpdatesPrompt
- Backups3-2-1, restore-tested
- Access2FA, least privilege
- URLsNever broken
Safeguarding a Journal Website: Habits for Editors and Staff
A journal website holds the scholarly record and the trust of its authors. Editors and small teams can reduce risk considerably with routine care, even without deep technical expertise.
- Test restoring from backups. Making copies is not enough; practise restoring one to a separate location. A backup that cannot be restored gives only false comfort.
- Limit who holds admin rights. Give each person only the access their role needs, and remove accounts when someone leaves. Fewer powerful accounts mean fewer ways in for attackers.
- Use strong, unique credentials. Encourage password managers and an extra sign-in step for editorial accounts. Reused passwords are one of the most common causes of takeover.
- Preserve article addresses. Avoid changing the web address of published papers when redesigning. Stable links keep citations working and protect readers from dead pages.
Restore-test your backups, restrict access sensibly and keep article addresses stable to protect the scholarly record.
Questions Researchers Often Ask
In Summary
Security and upkeep keep a journal website credible for the long term. Own your domain, choose reliable hosting, encrypt all traffic, apply updates quickly, follow the 3-2-1 backup rule and test restores, restrict access, stay alert to threats, provide each article a complete permanent page and guard your URLs. Even a short routine, followed regularly, prevents most disasters.
Your paper is ready? Submit it to JMVRA
JMVRA (ISSN 2984-8911) is a peer-reviewed, open access journal spanning many disciplines. Submission is free. Specialist reviewers assess your paper, and you receive the acceptance or rejection decision by email and WhatsApp.
- 1. Match your manuscript to the guidelines
- 2. Submit online
- 3. Peer review
- 4. Decision by email & WhatsApp
- 5. Appear in open access
References and Further Resources
Website Operations Summary
- DomainJournal-owned
- HTTPSEverywhere
- UpdatePromptly
- Back up3-2-1
- ProtectURLs and user accounts
Related: Pages and SEO · OJS setup · Submit Paper.
Ready to Publish? Submit to JMVRA
JMVRA is aligned with UGC's Suggested Parameters for Choosing Peer-Reviewed Journals.
JMVRA is a Transparent, Peer-Reviewed, Open Access Journal (Refereed Journal). Following the discontinuation of the UGC and UGC-CARE journal listing, and in alignment with the latest UGC-CARE recommendations and guidelines, JMVRA is aligned with UGC’s Suggested Parameters for Choosing Peer-Reviewed Journals.
Pages worth visiting on jmvra.org
Key Terms
Subjects and search phrases this article addresses.
Related Reading
Further guides on journal websites and their operation.
Pages Every Academic Journal Website Needs
Read the guide RelatedSetting Up Open Journal Systems for a New Journal
Read the guide RelatedArticle Metadata Checklist: Fields, Tags & Formats
Read the guide RelatedRepositories & Journal Archiving Explained
Read the guide RelatedJournal Hijacking: Spotting Cloned Journal Sites
Read the guide RelatedLaunching a Journal: 50 Items to Finish Before Issue 1
Read the guideKeep Reading on the JMVRA Blog
As part of the JMVRA journal blog, this guide shares practical help on publishing, indexing, metrics and research integrity, and is written to be verifiable rather than promotional.